Phone: +254 700 524589 | +254 782 524589 Email: [email protected]
October is Cybersecurity Awareness Month. For a long time, this felt like an IT topic. But that has changed. Cyber risk is now a governance issue. It belongs on the same table as financial risk and operational risk — right in front of boards, audit committees, and senior managers.
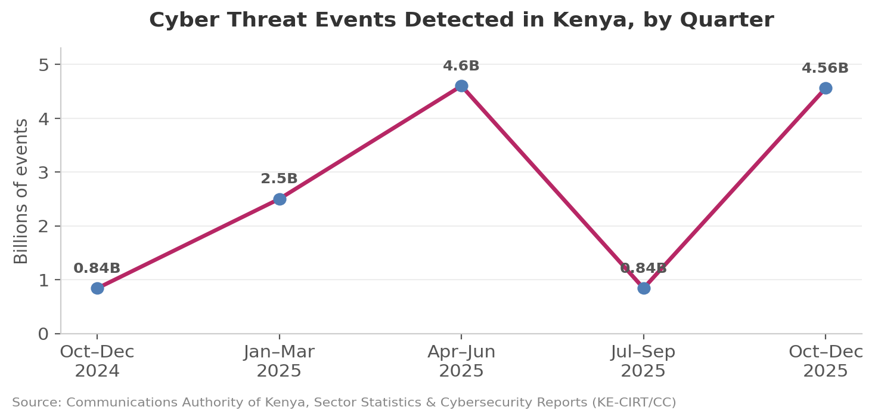
The numbers show why. Kenya’s cyberattacks rose sharply in early 2025. Threats climbed from 840.9 million to 2.5 billion in just one quarter. By June 2025, they hit 4.6 billion — the highest ever recorded in a single quarter. Then, surprisingly, threats dropped to 842.3 million the next quarter. But the calm did not last. Between October and December 2025, threats spiked again, to 4.56 billion events.
So what does this mean for you? It means the risk is not going away. It means boards cannot treat this as a once-a-year topic. And it means six cyber risk questions for boards deserve a permanent place on every agenda.
1. What Are Our Top Cyber Risks, and Have We Assessed Them?
Every organisation faces different risks. A sacco worries about payment fraud. A hospital protects patient data. A college holds student records. But do you know your own biggest risk? And has anyone tested it?
Ask management three things. When was the last risk assessment done? What did it find? What changed afterward? At minimum, this review should happen every year.
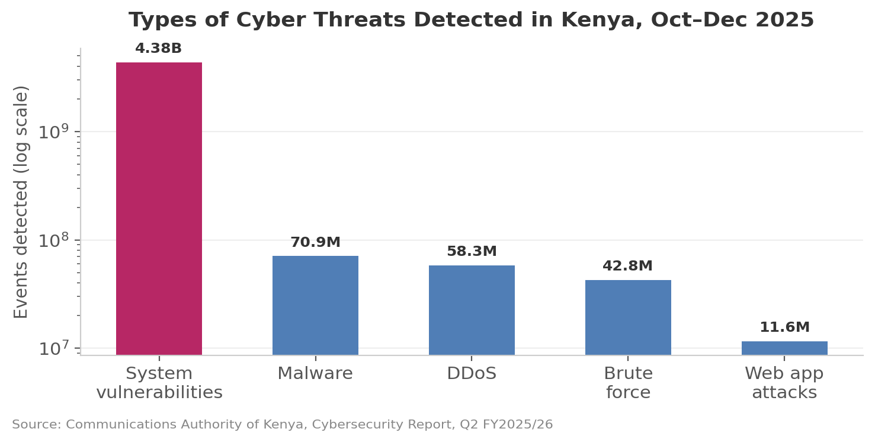
Nationally, the risk picture is clear. Look at the chart below.